2 hours ago
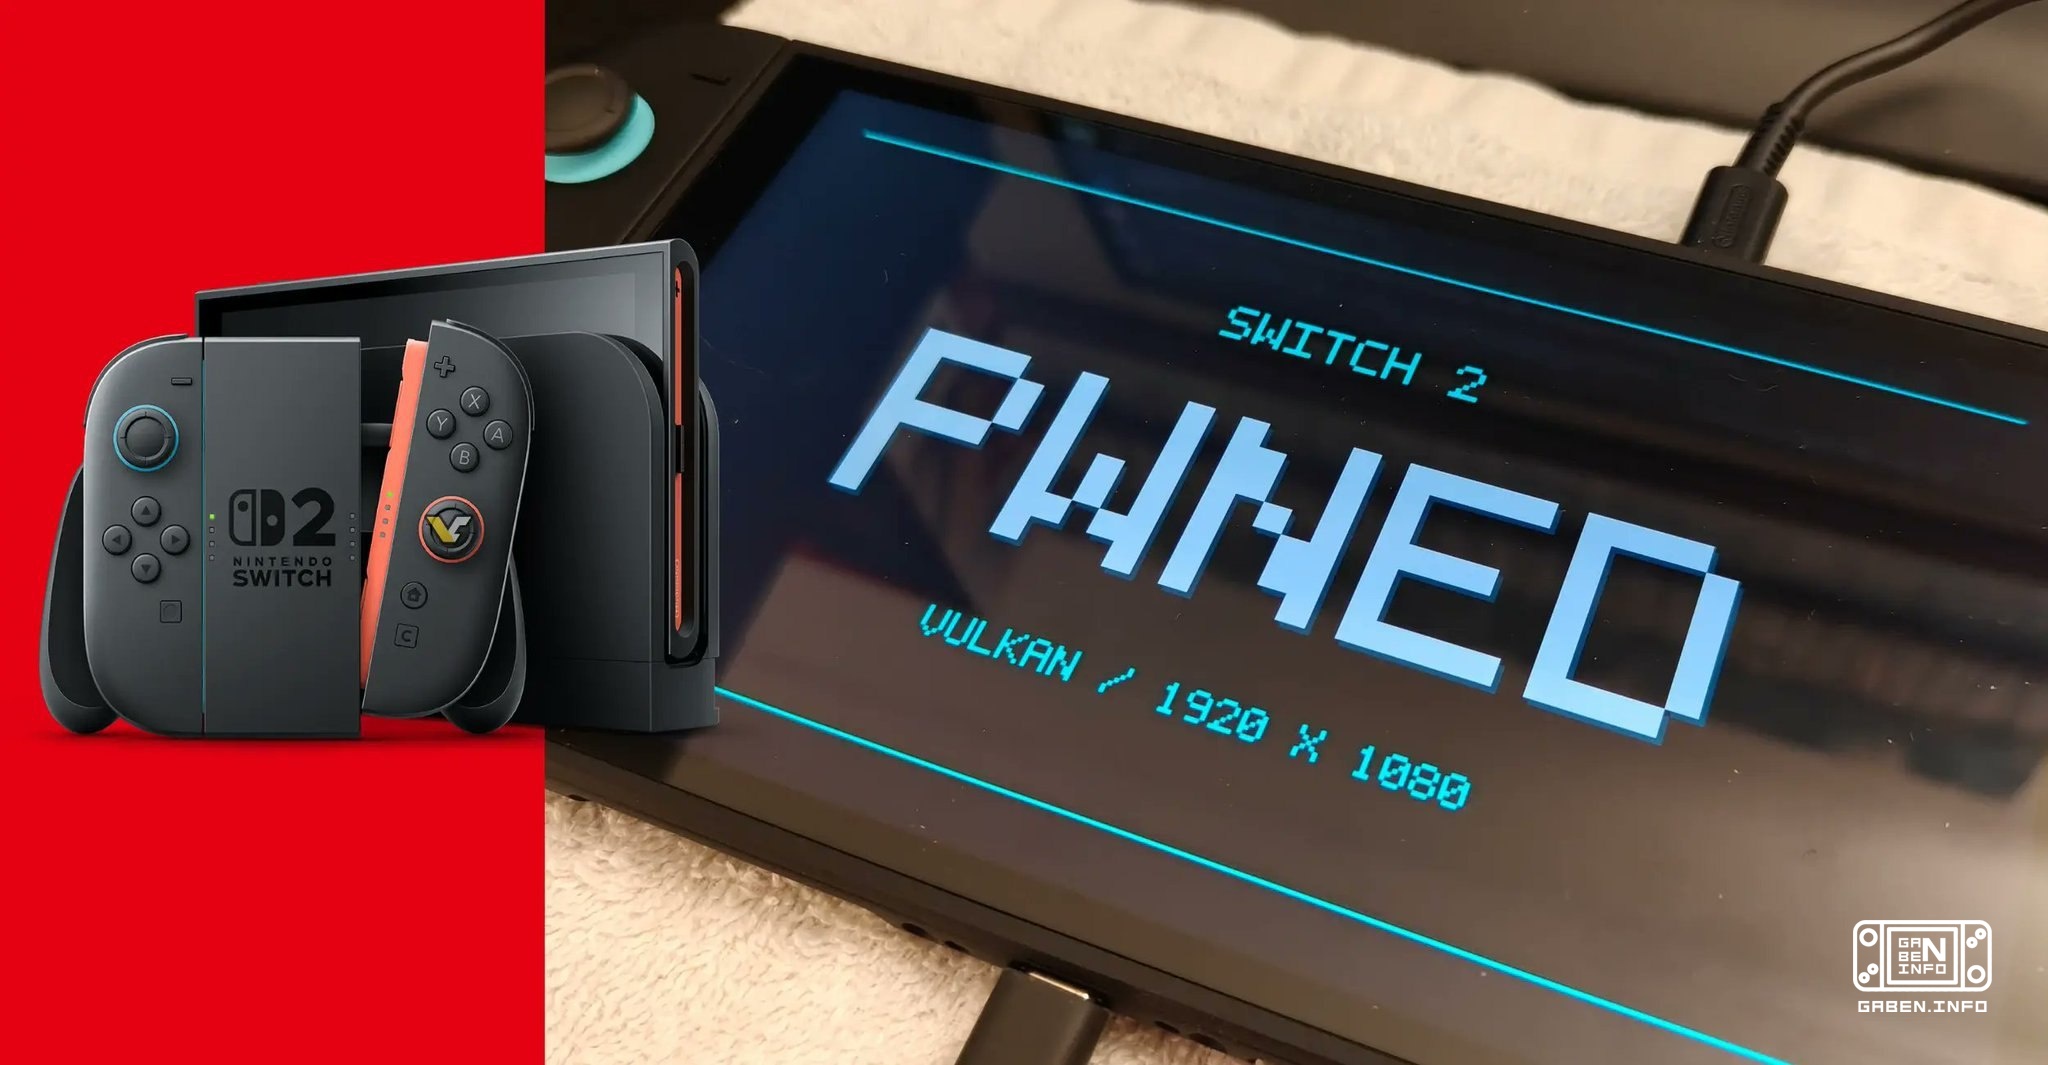
Atmosphère, nicknamed hexkyz, developed a new exploit for the Nintendo Switch 2, which was created by artifici
Atmosphère, nicknamed hexkyz, developed a new exploit for the Nintendo Switch 2, which was created by artificial intelligence.
Here's what the developer said:
• A vulnerability in the file system system module (hereinafter FS) was discovered many years ago, but hexkyz considered it unusable.
• The main obstacle was the organization of the FS memory. There were very few useful indicators in the heap. The operating method itself was also known: it was necessary to find the mechanism of creating IStorage objects in memory and to take control over their read and write indicators.
• The most difficult task was keeping the right objects in memory long enough. All previous attempts by developers to use other vulnerabilities ended up with empty memory areas.
• This is where AI made its main contribution. He invented a complex heap grooming sequence that allowed for the right location of objects. According to hexkyz, the AI code that came through is a practically unreadable nightmare, but it really works.
• After obtaining arbitrary reading and recording memory (arbitrary R/W) already known methods are used: setting the client PID to the value 1, MITM-intercept loader, obtaining foreign descriptors and other techniques.
• Access to FS allows you to extract virtually any binary files below KIP: games, applications, and system modules that are not KIP.
• It is not possible to obtain encryption keys or related material through FS.
• Further enhancement of privileges, such as access to the core, remains as difficult as operating any other system module.
• There is a potential for compromising other KIP modules. According to the developer, there is one method that the exploit authors did not consider in their publication and that could theoretically work.
• SmileBASIC is not required for hacking. The entry point can be a game for the first Switch, a game for the Switch 2 or even a browser. The exploit was originally created under SmileBASIC, so many will rush to acquire it, but the FS vulnerability is available almost everywhere.
• There are other unpublished vulnerabilities in older versions of firmware, which could potentially lead to further advancement in the system.
• There are other closed-end FS vulnerabilities, but the current one has been shown to be significantly more effective than the others. Hexkyz admits that this may be the only way to break the system so deeply in a very long time.
• The new operating chain actually became the modern analogue of nspwn with the first Nintendo Switch.
• Theoretically, the exploit can be turned into an unethered one that doesn't require a reboot after each reboot.
Separately, hexkyz explained whether Switch 2 owners should update the firmware.
On the one hand, it is an extremely powerful exploit that provides complete control over the user level of the system (userland). It is no longer possible to climb above the FS module within this level. However, anything outside the userland remains inaccessible.
On the other hand, full control of userland opens up opportunities for data mining, game modification and other similar actions, but exploit will most likely only remain available on firmware up to and including 23.0.1, as Nintendo will quickly remove the vulnerability. #game